Steve Penry
Energy & Commodity Consultant at Shield and Founder of SurveilEdge
An asset is about to go offline for unscheduled maintenance, taking supply out of the market. Before the Urgent Market Message (UMM) is published, somebody in the dispatch team speaks to the site and learns about the outage. The information is passed to the asset trading team, legitimately, because that desk hedges the plant’s expected output and its forecast has just changed. Nobody on that desk trades ahead of publication.
Then one person on the asset desk sends a WhatsApp message to somebody on the speculative trading desk. The speculative trader takes a position before the UMM goes out.
Trade surveillance will probably catch that activity. It can show you the orders, the timing, and how closely the trade sits against the UMM that followed. What it cannot show you is how the trader knew.
Everything that makes the scenario above a regulatory issue sits in a call and a message. Who passed the information on, and what the trader knew when they acted on the information.
Somebody has to be curious enough to ask. That is the quality I have always valued most in a surveillance team, and it is the hardest one to build into a system. A transaction or an order can look perfectly normal viewed in isolation, and a communication can look harmless until you know what was happening in the market at the time. The analyst who closes the case is the one who treats an alert as the start of a question rather than the answer to it.
Review the communications and the loop closes. The information originated at the site, moved through dispatch to the asset trading team, and was then shared with the speculative trader before it became public. That could raise issues under Article 3 of REMIT, which prohibits insider trading and the unlawful disclosure of inside information. Depending on the nature of the subsequent trading, Article 5 considerations could arise too.
If communications are not monitored, or certain channels are not being recorded at all, that reconstruction is not available. The investigation stops at the alert.
It helps to separate market abuse risk by what each data source can see.
Trade surveillance is well placed to identify unusual orders, shifts in trading behavior, potentially manipulative patterns, and activity that spans products or markets. All of that shows up in order and transaction data.
Other risks sit primarily in communications and may never generate a trade surveillance alert at all. Inappropriate information sharing, collusion, and conversations around confidential information fall into this category.
The analyst who closes the case is the one who treats the alert as the start of a question rather than the answer to it.
Then there is the overlap, which is where the difficult cases live. Take potential coordination across related gas-market activity. Trade surveillance may flag unusual patterns, timing, or behavior worth investigating, and it can show you the orders, the positions, and the relationship between the trades. What it will not tell you is whether the activity was coordinated, what information was being shared, or what sat behind the decision to trade.
Where coordination, knowledge, or intent is the question, communications surveillance supplies the answer: what was known, when it was known, and who spoke to whom. Put that next to the trade data and the relevant physical-market information, and an alert that appeared straightforward in isolation can look very different.
The regulatory landscape has moved since the revised REMIT, and expectations around surveillance have moved with it. ACER’s latest REMIT Quarterly sets out how it intends to conduct cross-border investigations, which tells you something about where enforcement is heading. At the end of Q2 2026, 453 potential REMIT breach cases were under assessment. Firms are operating in an environment where regulators and market monitors have increasingly sophisticated data and surveillance capabilities of their own.
From an in-house perspective, I would much rather my team had already reviewed the relevant chat and listened to the call before a regulator asked about it. There is a very different conversation to be had when you can say “we identified this, investigated it, and took action” than when the investigation starts after the request arrives.
That means a firm must be able to show that its surveillance addresses the risks it faces, not that it inherited a set of controls nobody has looked at in years.
Nord Pool’s REMIT Best Practice Report is clear that there is no one-size-fits-all approach. Having run in-house surveillance teams across energy and commodity firms, investment banks, and broker-dealers, I think that is especially true of communications. Buying an off-the-shelf set of scenarios and assuming the risks are covered misses what the exercise is for.
The report’s current edition adds a section on monitoring requirements for persons professionally arranging or executing transactions, the population caught by Article 15 of REMIT. A lot of firms are still working out what “effective arrangements, systems, and procedures” is supposed to mean for communications rather than trades.
Start with the business. What is being traded, in which markets, and by whom. How information moves through the organization, which channels people actually use, and which market abuse risks the firm is genuinely exposed to. A gas and power utility operates differently from a global trading house, and both operate differently from a small renewable operator with a trading desk. Their risks differ, so their surveillance should too.
You can technically have access to the communications and still be badly served by it.
If I were explaining the framework to senior management or a regulator, I would be far more comfortable saying it was designed around the risks in our business than saying we use the same controls as everybody else.
Many firms already record and retain a great deal of what their recorded population says. The problem is usually what happens next. Voice sits in one archive, email in another, Teams somewhere else, and mobile messaging somewhere else again. WhatsApp is the hardest of all, because the traffic that matters most in a case like the one above is often the traffic that never touched a monitored channel to begin with.
I have seen the practical consequence of that. You can technically have access to the communications and still be badly served by it if an analyst has to jump between systems, search separate archives, and hand-assemble a timeline while trying to understand an issue quickly.
In the scenario above, that means finding one internal call and one WhatsApp message, in the right order, without knowing in advance that either exists.
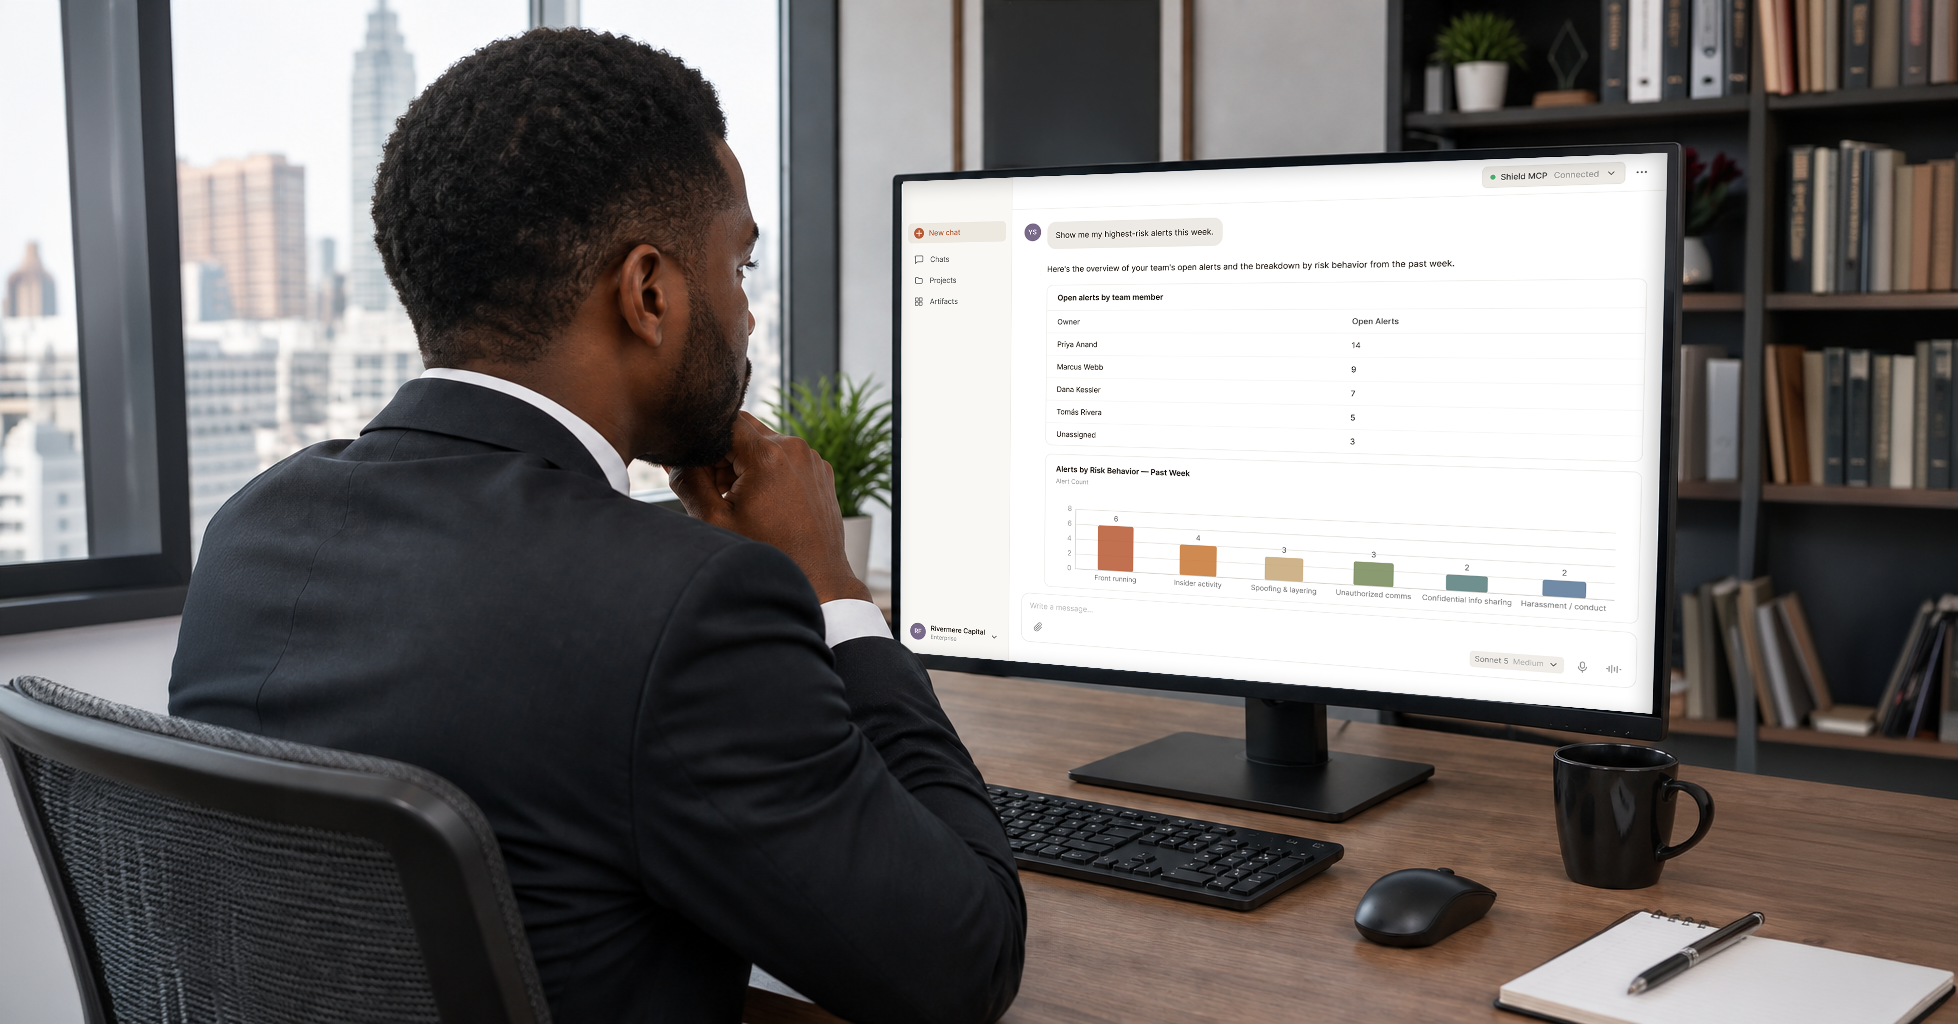
That is where communications surveillance should earn its place. It should make the investigation faster, not hand the analyst another system to fight with.
When trade and order data and relevant communications can be brought together quickly, the matter gets escalated to the right people, investigated properly, controls tightened where they need to be, and any required regulatory notification made promptly.
No surveillance framework catches everything. But being able to show that the right controls were in place, that they worked, and that the firm acted when something surfaced puts you in a far stronger position than starting from a standstill.
Trade surveillance can tell you that something happened. Communications surveillance is often the difference between seeing the alert and understanding the story behind it.
Learn how Shield’s AI-powered communication intelligence strengthens energy and commodities compliance.
Gain access to exclusive insights, industry influencers, and thought leaders in
Digital Communications Governance and Archiving (DCGA).