


History Made and Other Things I Learned at AFME
History was made Monday, September 21, 2026 at AFME (Association for Financial Markets in Europe) Compliance and Legal 2026. There, at a panel I moderated, we were discussing what constituted effective surveillance when a head of surveillance, at grave risk to himself, announced to the room that not all trade surveillance is able to be done T+1. Another surveillance head chimed in, echoing the sentiment. And then, unbelievably, a head of governance, also in assent.
Silence befell the room.
Heads turned to the regulator on the panel. Would he storm off? Would he overturn the table?
He did not.
Leaning into the mic he announced, acting in his own capacity of course, that he too often did not perform surveillance at T+1, that often it happened at T+3 or, blimey, T+5(!).
If the candor from the stage broke ground, its reasons for being were more practical. The admission came about during a discussion on the realities of data governance. It is a fact that not all data arrives on time. Bloombergs come in 2 or 3 days late. Batched communications versus continuous ones. Alerted risk and the story surrounding an alert is often incomplete as associated data arrives over days.
That means developing a program built on the premise of T+1 while maintaining controls that can account for delays. It’s a complexity equivalent to managing data completeness where firms and vendors like Shield have developed controls around expectations of completeness while having mechanisms to account for when files arrive corrupted or are riddled with upstream errors.
#whatwemeanwhenwesaygovernance
Again and again we returned to governance as the organizing mechanism for how complexity and controls meet.
And yet, what did we mean by governance?
More and more it has become a catch all. People it in place of policy. It’s always uttered, rightfully, in the same breath as AI. Carolina Montiel Alocen set everyone straight. Governance established accountability and oversight. Crucially, governance also included an important intangible: critical thinking and our ability to apply it to the ever increasing change compliance teams help bring order to.
There’s more!
#Non-FinancialMiscoduct
With the FCA’s regulations on Non-Financial Misconduct going live earlier this month the question put to the panel was straight up: should it be monitored in eComms and should that monitoring be expanded to other populations. On the first, the answer was definitive. Surveillance must be extended to surface non-financial misconduct across existing monitored populations.
But should it be expanded? Provisionally but not absolutely was the more qualified response. Which is to say the consensus is evolving. Likely more populations will be monitored for NFM but who and to what degree is still being understood.
#AIinCompliance
Another eye opener, this one on AI.
The question was, assuming (and we do) that AI capabilities will get to a place where they will vastly improve detection and automate review, which would surveillance leaders rather have. Would they rather:
Detection so fine-tuned it only returned results when actual risk was present
OR
Agents that automatically reviewed a corpus of alerts
Anish Kalraiya went first and from there consensus built. No one wanted just one alert. It goes back to that governance thing, to having a program you can evidence. Reviewing BAU and weaker signaled messages are a way to understand risk within a firm more broadly. Having a corpus of alerts is how we evidence a program in the first place.
#Offchannelcomms
Off Channel comms are still a thing though breaches can be better understood as governance (there goes that word again) failures and not the operational failures that came out of the original SEC fines. Viewed through that lens, they have not lost importance. Channels have only become even more complex and diffuse. But off channel risk can be viewed as normalized, a core part of surveillance functions.
And . . .
#DataSubmissions
Christophe Bonnet reminded us how important data quality had become to regulatory submissions. There was much praise here because the quality and consistency of the data is much improved from over the years. Which only makes gaps more glaring . . .
#GovernedAI
Finally, a view from the future.
We discussed an observation Paul Clulow-Phillips had made. With all the talk of AI, are we prepared for the day deployed AI get something wrong? We returned to governance. AI will undoubtedly get something wrong. You can count on it. How we surface, catalogue for and remediate those errors has to be accounted for now. It’s a mandate that is clear and that will require continued critical thinking to see through effectively.
#AFME2026
If AI errors were cause for concern, know that there are bigger, badder monsters out there. Top of the list was the effect quantum computing will have on modern encryption. Security apparatuses built over the past decades are not prepared. At the same time, the eventuality of quantum computing is certain.
That was the message Hanzo van Beusekom laid out in a speech otherwise concerned with a Europe that needed to further unite. If last year’s AFME concerned itself with divergence, this one accepted our world as diverged. The solution for Europe was to look inward and take the actions necessary to grow its economy.
For Marie-Anne Barbat-Layani that meant fostering the SIU strategy to unlock savings sitting idly in EU bank deposits.
Though partial responsibility for success of the strategy lies with the business community, there was general agreement among heads of compliance and regulators alike that simplification would help ease the path.
So said from Florent Palaysi from CACIB. So said Claudia Gonzalez Cabanillas from JP Morgan.
And the path to that path (follow me, if you will) was strategic alignment – simplified supervision, a European permission structure for tokenization – it all depended on the ability for European States to work together.
#acitywithaview
From the top floor of the hotel hosting AFME 2026, where we celebrated the conference’s tenth year, Paris was laid out before us with the Eiffel Tower photo bombing every selfie. The sun was setting. The champagne was crisp. Alignment felt palpable.
Looking forward to AFME 2027 when we’ll hear how that promise has advanced.
This article was originally published here.
Related Articles
6 Lessons From XLoD: Rethinking Surveillance for the AI Era
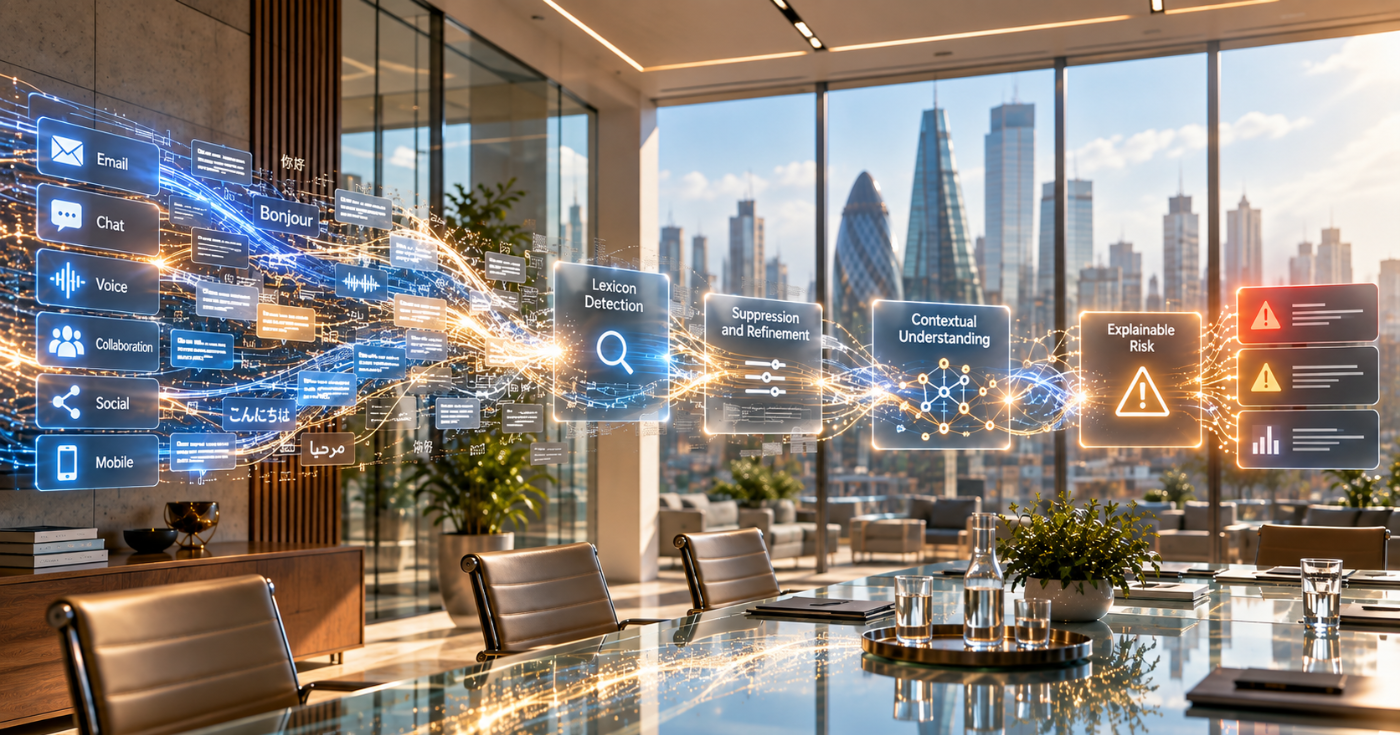
Lexicons, LLMs and AI Agents in Communications Surveillance: A practical guide to designing, testing, governing and modernizing communications surveillance using lexicons, LLMs and agentic AI
Subscribe to our newsletter
Gain access to exclusive insights, industry influencers, and thought leaders in
Digital Communications Governance and Archiving (DCGA).